Security Threats Don’t Stop at the Office: Why Executives’ Families Need Training Too
Those closest to executives must match their security postures because the weakest link in a family becomes the entry point for attacks.
Germany has arrested a Russian national suspected of being a leading member of the Qilin ransomware group following extradition from Japan earlier this month.
Should we be thinking more critically about letting devices get connected?
Flock would not say if CEO Garrett Langley would take a pay cut following the reduction in workforce.
Security researchers have published a full working exploit for a pre-authentication remote code execution flaw in AnyDesk Linux that gives attackers root access before anyone approves the connection.
Anthropic on Thursday unveiled OSS Scanner as an opt-in vulnerability scanner to help secure the open-source ecosystem using artificial intelligence (AI). “It’s an opt-in service informed by our experience using Claude to find vulnerabilities during Project Glasswing,” Anthropic said.
Threat actors have been observed exploiting two recently disclosed flaws in the AhsayCBS backup utility to seize control of affected devices and deploy web shells and XMRig cryptocurrency miners.
Attackers are exploiting a maximum-severity vulnerability in SonicWall SMA1000 appliances (CVE-2026-102255) that was patched on Tuesday, three days ago.
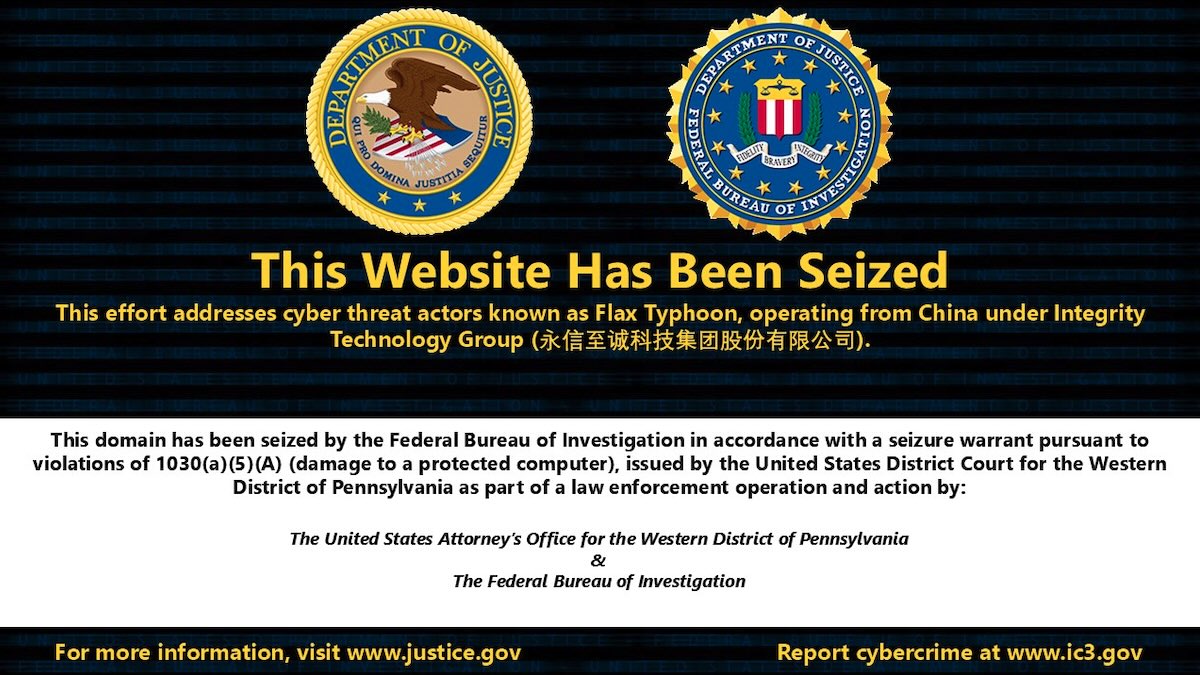
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Thursday added five security flaws to its Known Exploited Vulnerabilities (KEV) catalog, following their abuse by a China-linked threat actor known as Flax Typhoon.
Noteworthy stories that might have slipped under the radar: Tensorlake npm SDK compromised, Empire Market co-founder gets 40 years, exposed NVIDIA GPU monitors leak telemetry.
No word on exploitation status, but a 9.5 severity score suggests time is of the essence
As enterprises race to deploy autonomous AI agents to accelerate business, a new report reveals they are tethered to security architectures built for a different era.
The NBA legend, alongside other pro-basketball players, came out to demonstrate the blocking power of Next Gen Antivirus in a new way
Anthropic is offering open-source projects a new way to check for vulnerabilities with its OSS Scanner.
A Ukrainian-Russian dual citizen has pleaded guilty to running a massive money laundering operation that laundered millions for cybercriminals worldwide.
Approximately 66,000 unique entries are expected to emerge in 2026 , many boosted or even created by AI.
The flaws, CVE-2026-105133 and CVE-2026-105134, allow attackers to bypass authentication and inject OS commands.
Midnight Mimosa is the name given to a malware campaign primarily running preinstalled on low-cost Android devices.
A bug in GoBalance, a tool many dark-web sites use to stay reachable during attacks, lets anyone work out the secret key that controls a site’s .onion address using only public information, and then take that address over.
Flax Typhoon and other APTs used MicroScan and FishHub to scan and hack US and foreign critical infrastructure.
Citrix has warned IT administrators to patch systems immediately against a new critical vulnerability affecting NetScaler ADC networking appliances and NetScaler Gateway secure remote access solutions.
Citrix has released patches for yet another critical security flaw impacting NetScaler ADC and NetScaler Gateway that could result in remote code execution or denial-of-service (DoS) under certain conditions.
The security defect, tracked as CVE-2026-107406, could lead to remote code execution or denial-of-service.
$1.2 million was paid out at Pwn2Own Ireland 2026 for exploits targeting phones, printers, smart speakers, smart home hubs, and AI infrastructure and coding tools.
72 aktif kaynak
27 Türkçe · 45 İngilizce
Tüm kaynaklar