


Cybersecurity
US Disrupts Chinese State-Sponsored Hacking Tools
Flax Typhoon and other APTs used MicroScan and FishHub to scan and hack US and foreign critical infrastructure.
Flax Typhoon and other APTs used MicroScan and FishHub to scan and hack US and foreign critical infrastructure.
OSS Scanner sends unreviewed, model-generated vulnerability reports to open source maintainers that opt in.
The security defect, tracked as CVE-2026-107406, could lead to remote code execution or denial-of-service.
$1.2 million was paid out at Pwn2Own Ireland 2026 for exploits targeting phones, printers, smart speakers, smart home hubs, and AI infrastructure and coding tools.
Researchers from George Washington University have published a paper examining whether the time and cause of AI going rogue can be predicted.
The security defects could lead to unauthorized access, information leaks, privilege escalation, DoS attacks, and remote code execution.
All enterprises conduct security awareness training for their employees. But whether this has tangible benefits is debatable.
Threat actors have started targeting CVE-2026-21589, a critical vulnerability in Atlassian’s self-hosted Data Center products.
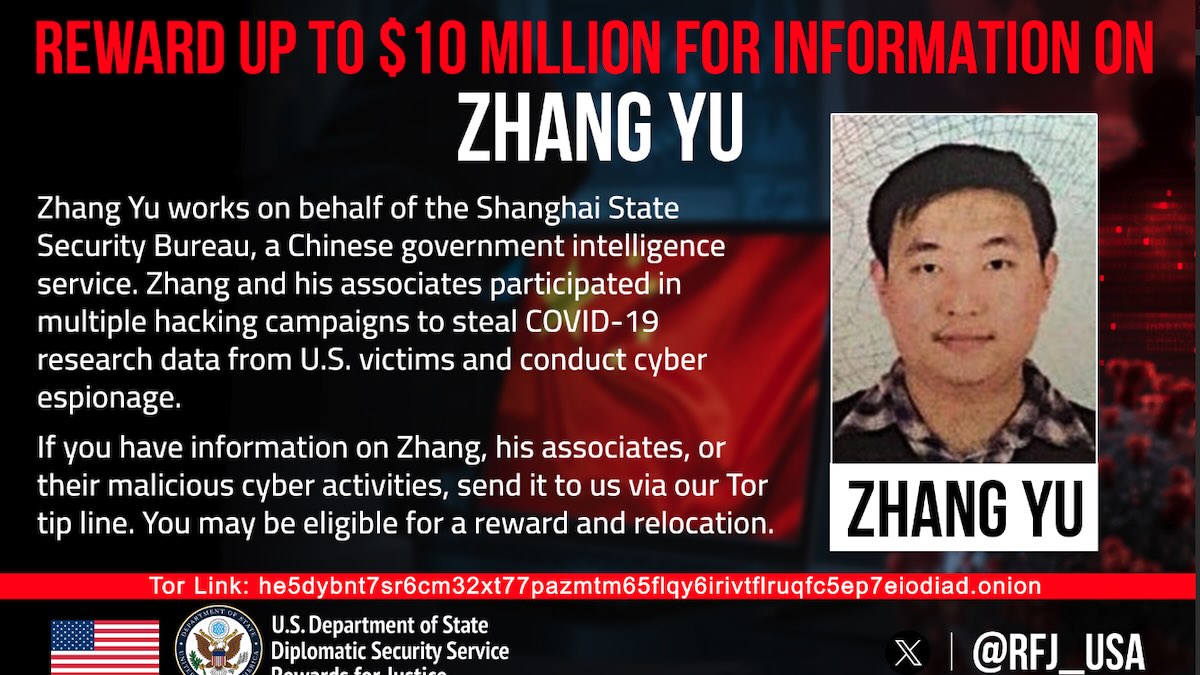
Zhang Yu was charged alongside Xu Zewei, who was extradited from Italy to the US in April 2026.
Critical and high-severity vulnerabilities could allow attackers to bypass authentication, execute arbitrary code, and elevate their privileges.

The cybersecurity startup will invest in product innovation, agentic research, and employee base expansion.
SEC Consult has published technical details on vulnerabilities mentioned in a complaint filed by several US states.
Zohar Pinhasi was paying ransoms to obtain decryption keys and then charging victims substantially more for remediation.
The figure is far higher than the counts that surfaced in earlier filings and patient notifications.
Attackers are creating new accounts and deleting existing ones and passwords to prevent legitimate access.
72 active sources
27 Turkish · 45 English
All sources







