Cybersecurity
Adobe Patches 140 Vulnerabilities Across 10 Products
The flaws affect products such as Commerce, Photoshop, ColdFusion, Substance 3D, Dimension, FrameMaker and Bridge.
The flaws affect products such as Commerce, Photoshop, ColdFusion, Substance 3D, Dimension, FrameMaker and Bridge.

Google is restructuring bug bounty rewards with a focus on complex memory safety vulnerabilities.
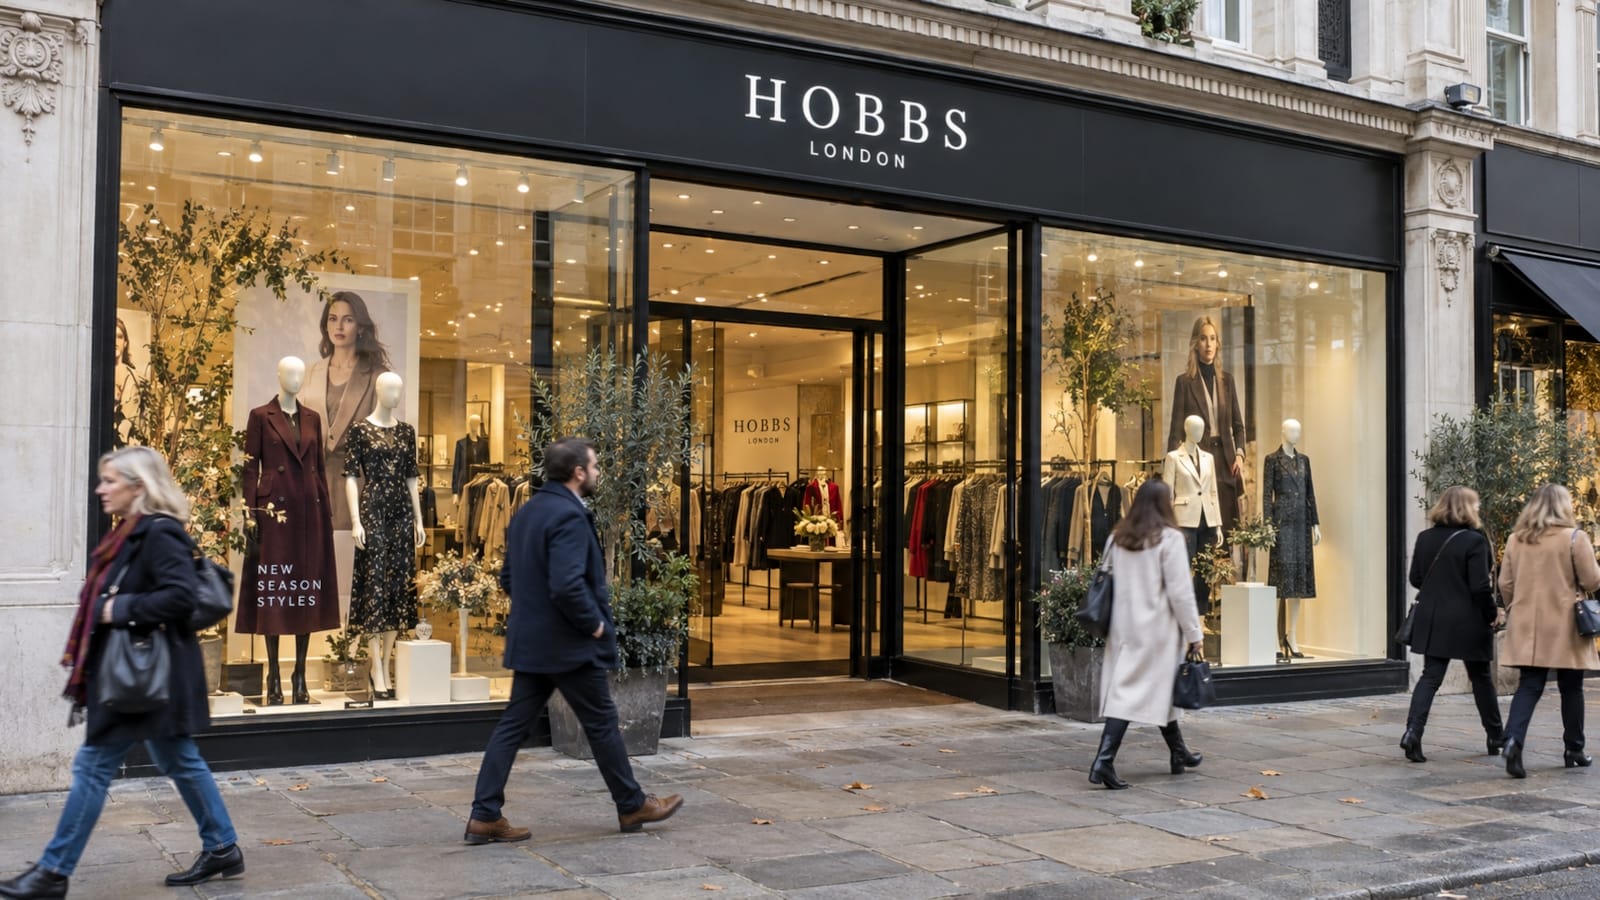
TFG London detected a cybersecurity incident that impacted IT systems used by the Phase Eight, Hobbs, and Whistles premium fashion brands.

GitHub has taken the step of expiring unvalidated npm trusted publishing configurations 48 hours after creation after researchers found that it was possible for an attacker to push new versions of a different user’s package without having to steal their credentials.
Most of the affected individuals are Meta employees in the United States and they are being offered credit monitoring services.

Impersonation Risk Detection uses on-device analysis and simple risk warnings to help protect you from scams.
Tracing where VPN breach data actually comes from

Ivanti urged customers on Tuesday to immediately patch an actively exploited zero-day vulnerability in the Ivanti Connect Secure (ICS) remote access gateway.

Docker has disclosed a critical vulnerability (CVE-2026-105445) in Docker Hub that let attackers access another user’s container repositories using a personal access token (PAT).
At least five organizations were targeted by the malware in just a few days.
Ahold Delhaize loses its hold on cybersecurity once again, as retailers report trouble operating.

Attackers continue exploiting gaps in MFA coverage, using stolen credentials to access VPNs, RDP, and Windows systems that still rely on passwords alone. Specops explains why protecting cloud applications isn’t enough and how organizations can close these authentication gaps.

SAP has addressed 20 security flaws across multiple products in its October 2026 security updates, including a maximum-severity vulnerability in the Cloud SDK for Python.
The Danish Central Register of Persons (CPF) was breached through the account of an IT and data services business. The hacker claimed that one of the breached accounts was only protected by a ‘123456’ password.

The Norwegian Data Protection Authority (DPA) has fined Xandr, an advertising unit owned by Microsoft, €8.6 million ($9.62 million) for illegally relaying Grindr users’ sensitive data to advertisers.
Google assured me that its algos are ‘designed not to log or store sensitive women’s health-related events’.
Daiichi Kosho had outsourced the handling of its customers’ personal information to NCG.
Stock spoiled at hundreds of stores as manufacturer says affected equipment ran outdated firmware

The dangerous part of a stolen identity isn’t always the initial login. It’s what an attacker can do with that access next. With AI accelerating reconnaissance, exploitation of vulnerabilities, and privilege escalation, attackers can move through systems faster than security teams can investigate.
Local media reports three weakly protected accounts at small IT biz whose access to national register was abused
Expanded plugin count allows the malware to monitor users’ location, stream live audio, and interact with authenticated browser sessions.

Three vulnerabilities in LG’s webOS can be chained to give an attacker on the same local network root access to certain smart TVs without a PIN or any interaction from the owner. LG has issued a fix, according to an advisory published by SSD Secure Disclosure on October 12.
IBM’s Steve Wallin talks to SecurityWeek on the effect of AI-driven attacks on enterprise defenses.
Without passwordless systems, threat actors will continue to undermine digital trust.
72 active sources
27 Turkish · 45 English
All sources