Cybersecurity
Are AIs Still Struggling with CAPTCHAs?
Anthropic’s recent security-incident document contains a bit about how CAPTCHAs are still frustrating Claude.
Anthropic’s recent security-incident document contains a bit about how CAPTCHAs are still frustrating Claude.

In a hearing today, Apple challenged the UK government’s refusal to publicly confirm whether it has issued an order requiring…

Canva, kurumsal kullanıcıları doğrudan etkileyen ciddi bir veri güvenliği kriziyle karşı karşıya. Kişisel Verileri Koruma Kurumu (KVKK) tarafından yayımlanan resmi bildiriye göre platformda kullanılan üçüncü taraf bir araca yetkisiz erişim sağlandı.
This essay was written with Nathan E. Sanders, and originally appeared in The Guardian. There are plenty of signs that AI will make all of our experiences of the US midterm elections worse. Voters have anxiety about AI’s impacts on the country. Politicos are using AI deepfakes to spread lies.
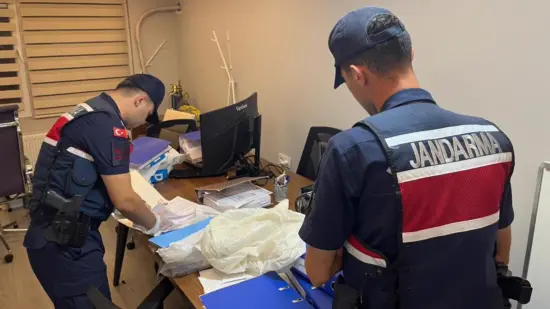
Milli İstihbarat Teşkilatı (MİT) koordinesinde, Siber Güvenlik Başkanlığı (SGB) ve Jandarma Genel Komutanlığı (JGK) iş birliğiyle Ankara merkezli Aydo Yazılım şirketine yönelik operasyon düzenlendi.
Kurumlarda üretken yapay zekâ kullanımının hızla artmasıyla birlikte hassas veri sızıntısı riskleri de tırmanışa geçti.
New variant of an old scam: Use the framing of a CAPTCHA to get an unsuspecting user to download and run a malicious program.
This essay was written with Cindy Cohn, and originally appeared in Lawfare. One of the many legacies of the terrorist attacks of Sept.
Really interesting story about Harvest, a specialized code breaking computer built in the 1960s by IBM for the NSA.
Skullcandy Dime 3 kulaklıklardaki kritik Bluetooth güvenlik açığı, cihazların izinsiz eşleşmesine neden oluyor. Güncelleme yolu bulunmuyor.
If you’re on the fence about installing macOS 27 Golden Gate, Apple’s lengthy list of security fixes might be enough…
This is a current list of where and when I am scheduled to speak: I’m speaking online (via Zoom) at a League of Women Voters event on Tuesday, September 22, 2026 at 5 PM ET. I’m speaking at CanSecWest 2026 in Vancouver, Canada.
Smells awful: But an estimated 30 to 50 tons of dead squid remain inside the boat’s catch tank, where they have been decomposing for days. “That is nasty. I wouldn’t want to do that,” said commercial fisherman Dick Ogg of the Bodega Bay Fishermen’s Marketing Association.
Last month, I gave a talk at DEF CON on AI hacking: what happens when AIs become hackers. It’s a combination of the potentialities I raised in my 2022 book A Hacker’s Mind and the lessons we’re learning from current AI models engaging in hacking behavior.
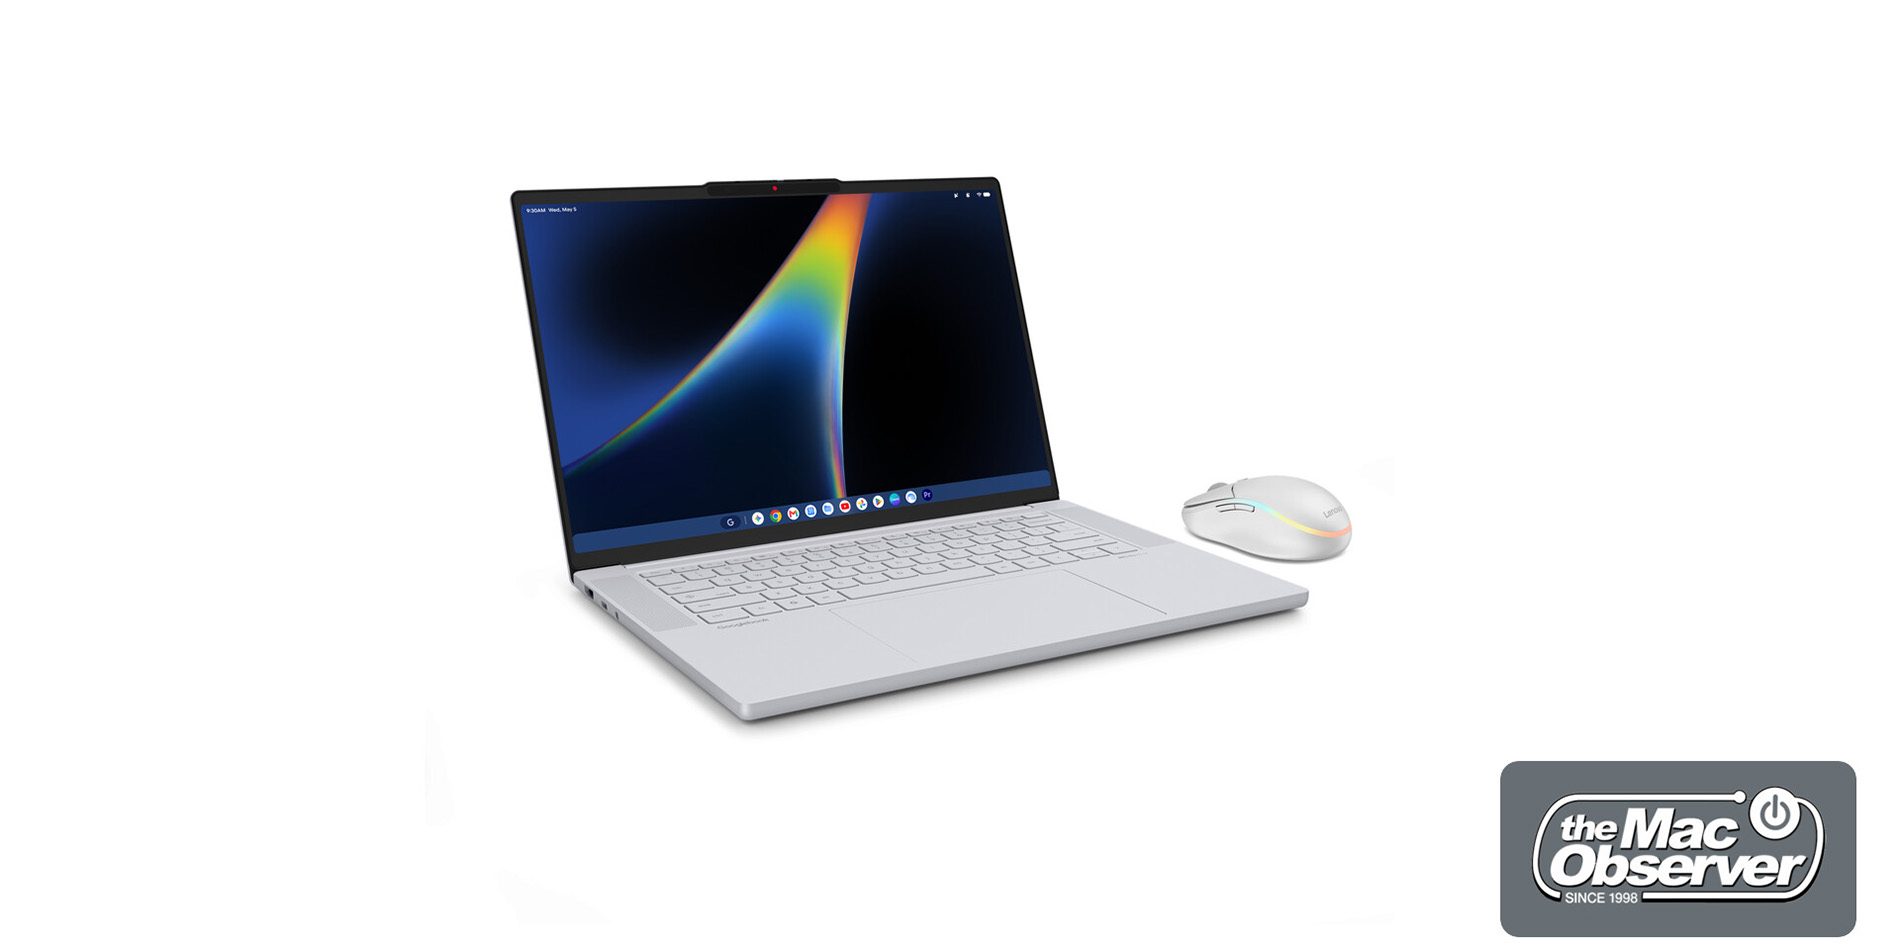
Following some past leaks, another new report reveals basically everything about the upcoming “Lenovo Googlebook 15” including its full specs,…
In August, Cliff Stoll gave a talk at DEF CON, remembering the wily hacker he stalked forty years ago. Great fun.

Ryan chats with Sam Curry, CSO at Zscaler, about where human intelligence sits in the new security landscape with AI, why shifting security protections closer to applications helps limit probes for vulnerabilities, and why building more resilient code infrastructure is the best way to address the…

GTA 6 sahte oyun dosyaları ile yayılan zararlı yazılımlar artıyor. Siber güvenlik uzmanlarının uyarılarını ve korunma yöntemlerini inceleyin.

KVKK, 80ler akımı ve benzeri yapay zeka uygulamalarında biyometrik verilerin işlenme riskine karşı kullanıcıları uyardı. Detaylar haberimizde.
Give an AI agent a mere rumor of an exploit, and it’s enough for them to find it. What’s worse, I found I could use my own agents to find the exploit just by knowing roughly what it was about and so could have been exploiting it well before the public patch was available!
Google has open-sourced Mantis, a stack-agnostic toolkit of security review skills for AI coding agents. It runs the full vulnerability lifecycle: sweep the code, filter false positives, reproduce the bug in a sandbox, patch it, re-attack the patch, then score the risk.
A database of 153 million drivers licenses is for sale on the dark web. Brian Krebs has more detail.
Claude Fable 5.1 solved a 370-year-old cipher in forty-four minutes. This tracks with what I wrote about AIs doing mathematics: It’s good at things that involve lots of searching and testing. EDITED TO ADD (9/14): I’m not sure if this result is correct. The blog comments have more discussion.
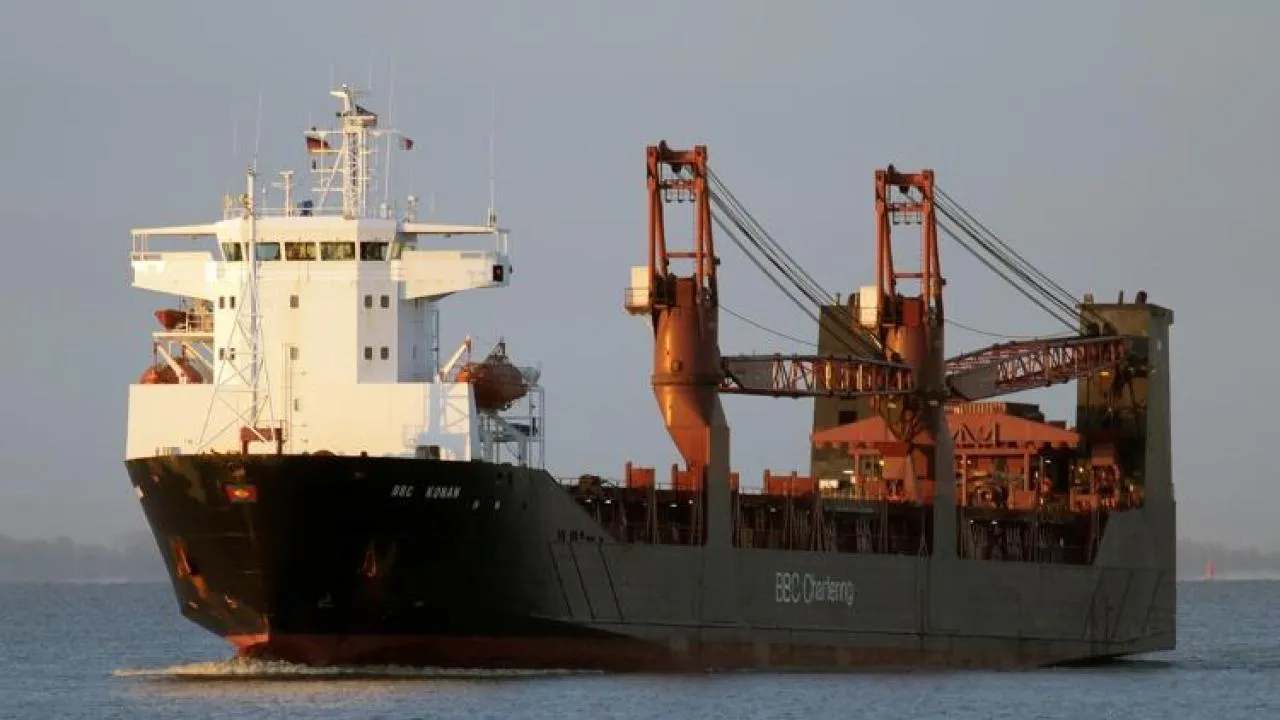
Akdeniz’de Rusya’nın askeri lojistik hatlarına yönelik dikkat çekici bir saldırı gerçekleşti. Rus bayraklı Lady Mariia adlı ro-ro kargo gemisi, 6 Eylül’de Girit açıklarında kamikaze insansız hava araçlarının hedefi oldu.
72 active sources
27 Turkish · 45 English
All sources