Cybersecurity
Cartoon Network Classics Exposed in Massive Leak
‘Regular Show,’ ‘Teen Titans,’ and other shows are caught up in a gigaleak spanning decades of Cartoon Network history.
‘Regular Show,’ ‘Teen Titans,’ and other shows are caught up in a gigaleak spanning decades of Cartoon Network history.

Daiichi Kosho, a major Japanese entertainment system maker, disclosed that a malware infection at its contractor, Nippon Columbia, exposed more than 8.7 million customer and employee records.
Lumen’s Black Lotus Labs says PoeLLM malware has hit more than 3,400 servers, most of them exposed AI tools like LiteLLM and Ollama.
He published a book on handling cyber extortion last month.
OrcaRouter released OrcaCyber Zero 1.5, a gated cybersecurity model with a 1M-token context window. It reports 100% on Cybench and 95.8% on an evaluable CVE-Bench subset, priced at $3.00 / $7.50 per 1M tokens.
Appointment or renewal reminder appears in victims’ calendar to lure them into logging in to fake Google, Microsoft or PayPal page You’re preparing for the week ahead and take a look at your Google calendar. There’s an entry for a meeting that you must have completely forgotten.

Enerji altyapılarına yönelik siber saldırı riskleri artarken Romanyalı Enevo, güneş santralleri ve elektrik şebekelerindeki şüpheli hareketleri tespit eden SentryOT platformunu geliştirdi.

The King spoke of “threats to our international order” in a letter marking the 10th anniversary of the National Cyber Security Centre.

Canadian cybersecurity executive Edward Dubrovsky has been arrested in Pennsylvania in connection with alleged extortion activity that multiple reports have linked to the FBI’s ongoing crackdown on the ShinyHunters hacking group.
A VPN masks where you are – not what you share
The cyberattacks that shook the South Korean financial sector earlier this month were launched by a Chinese hacker using the ARTEX AI penetration testing suite and Claude agents.
Traditional attack surface management helps organizations discover exposed assets, but visibility alone is not enough to address threats. Criminal IP introduces AITEM, an AI-powered approach that connects exposure discovery with investigation, risk prioritization, and response.

Güvenli olduğu için kripto varlıklarını soğuk cüzdanlarda taşıyanlara soğuk duş. Ünlü LEdger markasının belirli cüzdan modellerine siber saldırı yapıldı.

In environments studied for the 2026 State of Agent Security Report, roughly 1,280 third-party products now embed AI. About 282 of them sit behind single sign-on.
The former core infrastructure engineer deleted admin accounts, reset hundreds of passwords, and demanded 20 bitcoin to spare the company’s servers.
iPhone’ları hedef alan P7 DarkSword casus yazılımı, kişisel verileri ve parolaları çalıyor. Güncel iOS sürümleriyle cihazınızı koruyun.

Agents with the Federal Bureau of Investigation (FBI) on Thursday arrested the co-founder of a Canadian cybersecurity firm in connection with an investigation into the ShinyHunters hacking group that recently relieved the FBI of sensitive data on thousands of agents, multiple sources tell…
The attack on the British retailer shows that compromising a single identity can lead to much deeper penetration of the corporate network.

Hackers are abusing legitimate Bing search-result redirects as click URLs in Google search ads to direct users to fake Claude installers that deliver ClickFix attacks.
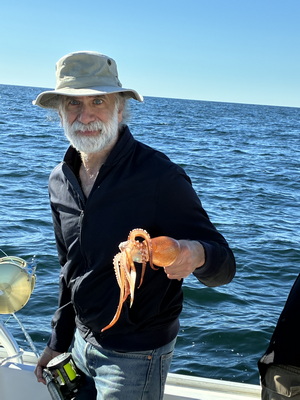
On Wednesday I spent a day fishing, on a small boat out of Gloucester, MA. We caught many cod (none of which we could keep), and a bunch of hake and mackerel (all of which we could keep). And…I caught a squid!
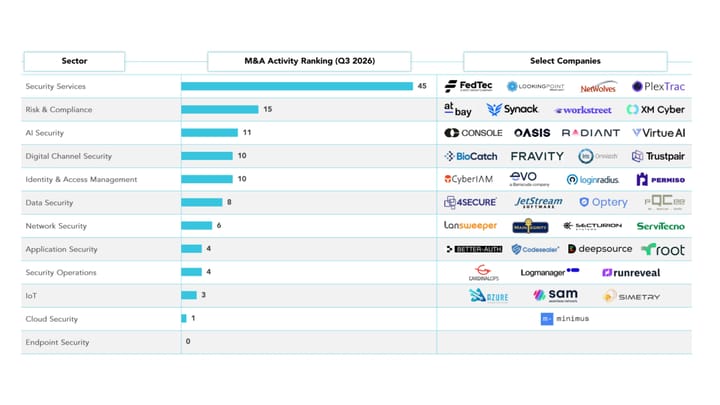
Welcome to another gangbuster year for strategic M&A activity in cyber, with 117 deals announced in the latest quarter. What’s different: Many of the buyers are not your typical cybersecurity firms.

Tokens transmitted in metadata, weak VM isolation, and expansive permissions make hacking a lot easier
72 active sources
27 Turkish · 45 English
All sources