Cybersecurity
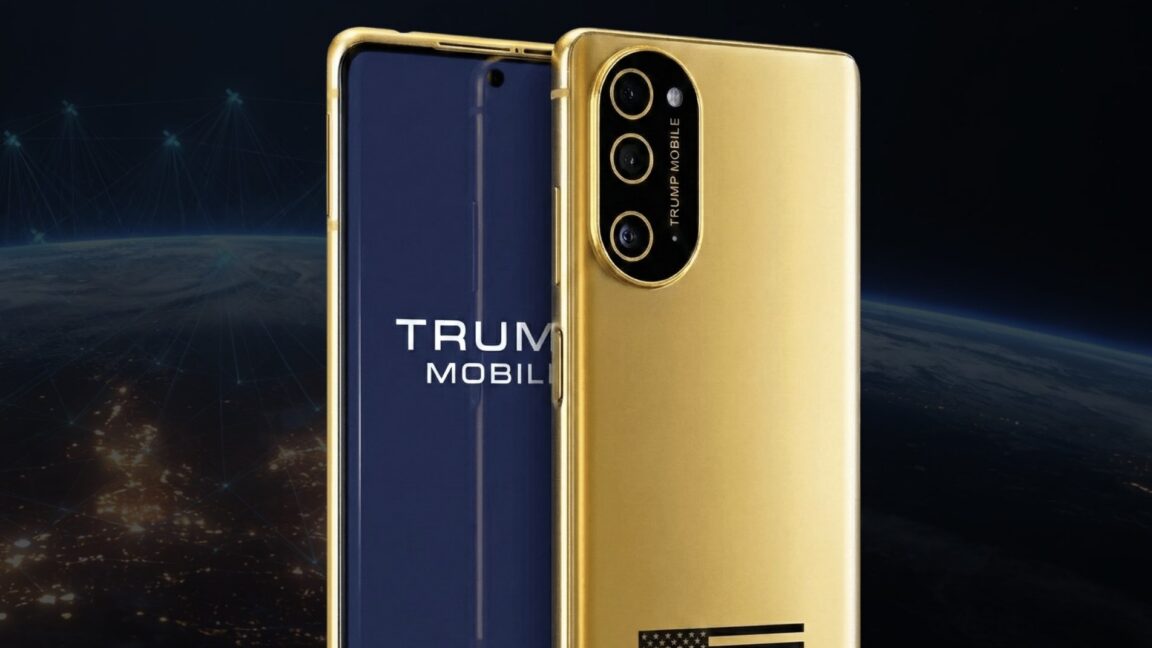
Trump Mobile hack and apparent lack of FCC authorization raise security alarms
After hack and data breach, senator asks why Trump Mobile lacks some FCC filings.
After hack and data breach, senator asks why Trump Mobile lacks some FCC filings.

Siber güvenlik şirketi Bitdefender, 8 Ekim 2026’da yayımladığı raporda bazı ucuz Android telefonların kutudan zararlı yazılımla çıktığını açıkladı.
IDC Frontier, a major Japanese cloud and digital infrastructure company, disclosed that its IDCF Cloud service was targeted in a ransomware attack that caused an outage at a data center cluster serving the eastern part of the country.
A malware campaign dubbed ‘Midnight Mimosa’ has been discovered on low-cost Android smartphones that ship with malicious software embedded in their firmware, allowing attackers to silently install apps, perform ad fraud, and turn devices into residential proxies.
The first cybercriminal to ever make the FBI’s “10 Most Wanted Fugitives” list allegedly infused Tren de Aragua’s violent criminal operations with cash.

Hackers tied to a Chinese cybersecurity company stole email from government organizations, law enforcement agencies, healthcare systems, and religious institutions in Southeast Asia, the FBI and agencies in 6 other countries said on October 8. The company, Integrity Technology Group, has been…
Cyber-espionage actor UAC-0099 has been steadily refining its flagship dropper in campaigns targeting Ukrainian organizations.

The crooks have trust problems of their own. One ransomware affiliate decided to keep the profits for himself. Elsewhere, an attacker left a server exposed, complete with tools and traces of an intrusion. Apparently, keeping things secure is a problem on both sides of the fence.
The censorship-busting VPN turns six with a spin-the-wheel promo, offering free premium access and exclusive discounts
More than 17,000 fake repositories on GitHub are distributing the SmartLoader malware after the FakeGit campaign reactivated earlier this month to push the StealC infostealer.

Retailer issues update after BBC contacted by cyber criminals who said this week’s breach went beyond “basic contact details”
Researchers corroborate parts of Silent Ransom Group dump detailing crypto payouts, cash brokers, and recruitment
A malware hunts for hidden messages in poems posted on GitHub.
The security defects could lead to unauthorized access, information leaks, privilege escalation, DoS attacks, and remote code execution.

The Russia-aligned threat actor known as UAC-0099 has been attributed to a previously undocumented .NET infostealer and remote access trojan (RAT) codenamed ASHVEIN. According to TrendAI, the malware has been put to use in attacks targeting Ukrainian government personnel. The cybersecurity company…
Cisco released security advisories for five critical vulnerabilities in its NX-OS data center network operating system that could be exploited to run arbitrary code with root privileges on Nexus switches.

Lavish homes, cars, watches, and hundreds of gold bars - definitely the lifestyle of an average CIA employee.
IPVanish is transforming from a standalone VPN into a comprehensive digital security suite. The provider has launched a next-gen antivirus built directly into its desktop apps, alongside three flexible subscription tiers to better match users’ privacy needs.

The hackers alerted the fashion giant’s customers through a push notification that said they had “fully compromised” the company’s cloud storage.
SPONSORED FEATURE: Old attack, new protections
All enterprises conduct security awareness training for their employees. But whether this has tangible benefits is debatable.
Three country-code top-level domains were hijacked and used to impact several leading global brands.

Cybersecurity researchers have disclosed details of a targeted campaign aimed at South Korean financial organizations that used an artificial intelligence (AI) pen testing tool named ARTEX to carry out the attacks. The activity, per CrowdStrike Intelligence, was active from late September to early…
Threat actors have started targeting CVE-2026-21589, a critical vulnerability in Atlassian’s self-hosted Data Center products.
72 active sources
27 Turkish · 45 English
All sources