Cybersecurity
‘This is a first for us’: Attackers uses poem to infect thousands of servers with malware
A malware hunts for hidden messages in poems posted on GitHub.
A malware hunts for hidden messages in poems posted on GitHub.
The security defects could lead to unauthorized access, information leaks, privilege escalation, DoS attacks, and remote code execution.

The Russia-aligned threat actor known as UAC-0099 has been attributed to a previously undocumented .NET infostealer and remote access trojan (RAT) codenamed ASHVEIN. According to TrendAI, the malware has been put to use in attacks targeting Ukrainian government personnel. The cybersecurity company…
Cisco released security advisories for five critical vulnerabilities in its NX-OS data center network operating system that could be exploited to run arbitrary code with root privileges on Nexus switches.

Lavish homes, cars, watches, and hundreds of gold bars - definitely the lifestyle of an average CIA employee.
IPVanish is transforming from a standalone VPN into a comprehensive digital security suite. The provider has launched a next-gen antivirus built directly into its desktop apps, alongside three flexible subscription tiers to better match users’ privacy needs.

The hackers alerted the fashion giant’s customers through a push notification that said they had “fully compromised” the company’s cloud storage.
SPONSORED FEATURE: Old attack, new protections
All enterprises conduct security awareness training for their employees. But whether this has tangible benefits is debatable.
Three country-code top-level domains were hijacked and used to impact several leading global brands.

Cybersecurity researchers have disclosed details of a targeted campaign aimed at South Korean financial organizations that used an artificial intelligence (AI) pen testing tool named ARTEX to carry out the attacks. The activity, per CrowdStrike Intelligence, was active from late September to early…
Threat actors have started targeting CVE-2026-21589, a critical vulnerability in Atlassian’s self-hosted Data Center products.
OAuth grants create data highways between SaaS apps, AI agents, and other tools. And, they are multiplying faster than any security team can review them. As the recent Klue breach showed, attackers are taking notice and exploiting forgotten OAuth grants to gain access to corporate data.
Suspected Chinese speaker used Claude Code and agentic pentesting tool ARTEX in attacks on South Korean lenders
A Maryland man was found guilty of stealing more than $53 million after hacking the decentralized crypto exchange Uranium Finance twice in April 2021.
Midnight Mimosa malware arrives pre-served.
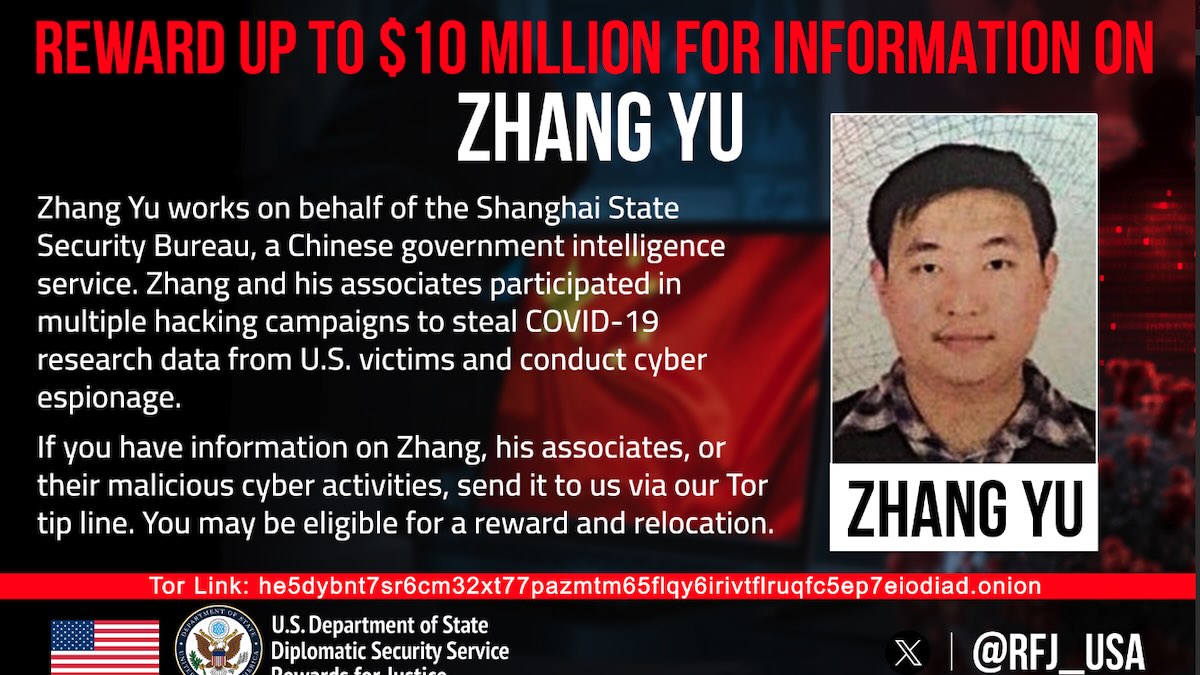
Zhang Yu was charged alongside Xu Zewei, who was extradited from Italy to the US in April 2026.
Critical and high-severity vulnerabilities could allow attackers to bypass authentication, execute arbitrary code, and elevate their privileges.
Microsoft will soon introduce support for third-party deepfake detection solutions and impersonation protection in Teams meetings.
The United States Department of Justice has charged Zohar Pinhasi, 50, also known as “Zack Silver” and “Zack Green,” with fraud. He ran a Florida-based company called MonsterCloud that told ransomware victims not to pay attackers because it had a way of decrypting their files – for a fee, of course.
Yapay zekâ destekli müzik dolandırıcılığı yaparak 8 milyon dolar kazanan Michael Smith, 18 ay hapis cezasına çarptırıldı. Detaylar haberimizde.
Dark Reading is about to begin a new decade in its storied history, and we have some breaking news of our own to share.
ASOS is sending updates to affected customers about the cybersecurity incident it suffered earlier this week, confirming that hackers accessed some personal data.
Security pact promises information-sharing and coordinated disruption, but offers little detail on agencies or funding
72 active sources
27 Turkish · 45 English
All sources