

Experts uncover bizarre new malware that spooks users with jump scares and screams
TechRadar (1 hour ago)

As if Windows 11 wasn’t scary enough on its own.
Read the full story on TechRadar.
TechRadar (1 hour ago)
As if Windows 11 wasn’t scary enough on its own.
Read the full story on TechRadar.

Threat actors are exploiting a critical command execution flaw, now tracked as CVE-2026-110447, in the Collabora Online - Built-in CODE Server app (richdocumentscode) for Nextcloud.

A newly disclosed critical flaw in the Linux kernel allows code inside a virtual machine to read memory on the host computer it runs on. A researcher demonstrated the leak against Vercel’s live cloud sandboxes, and Vercel confirmed it.

Someone built a tool to steal data, then decided it should scare the victim for fun. Yes, that’s an actual feature. And somehow, it fits right in with this week’s security stories. The rest gets interesting in different ways. A small permission can lead to a big theft.
A proxyjacking campaign has impacted devices in 34 countries, monetizing victims’ internet connections through a commercial residential proxy network.

Contextual defense helps security teams connect the signals, anticipate what comes next, and stop threats before they escalate.

A threat actor uploaded malicious packages to the Arch User Repository (AUR) that impersonated two popular helper tools, yay and paru.
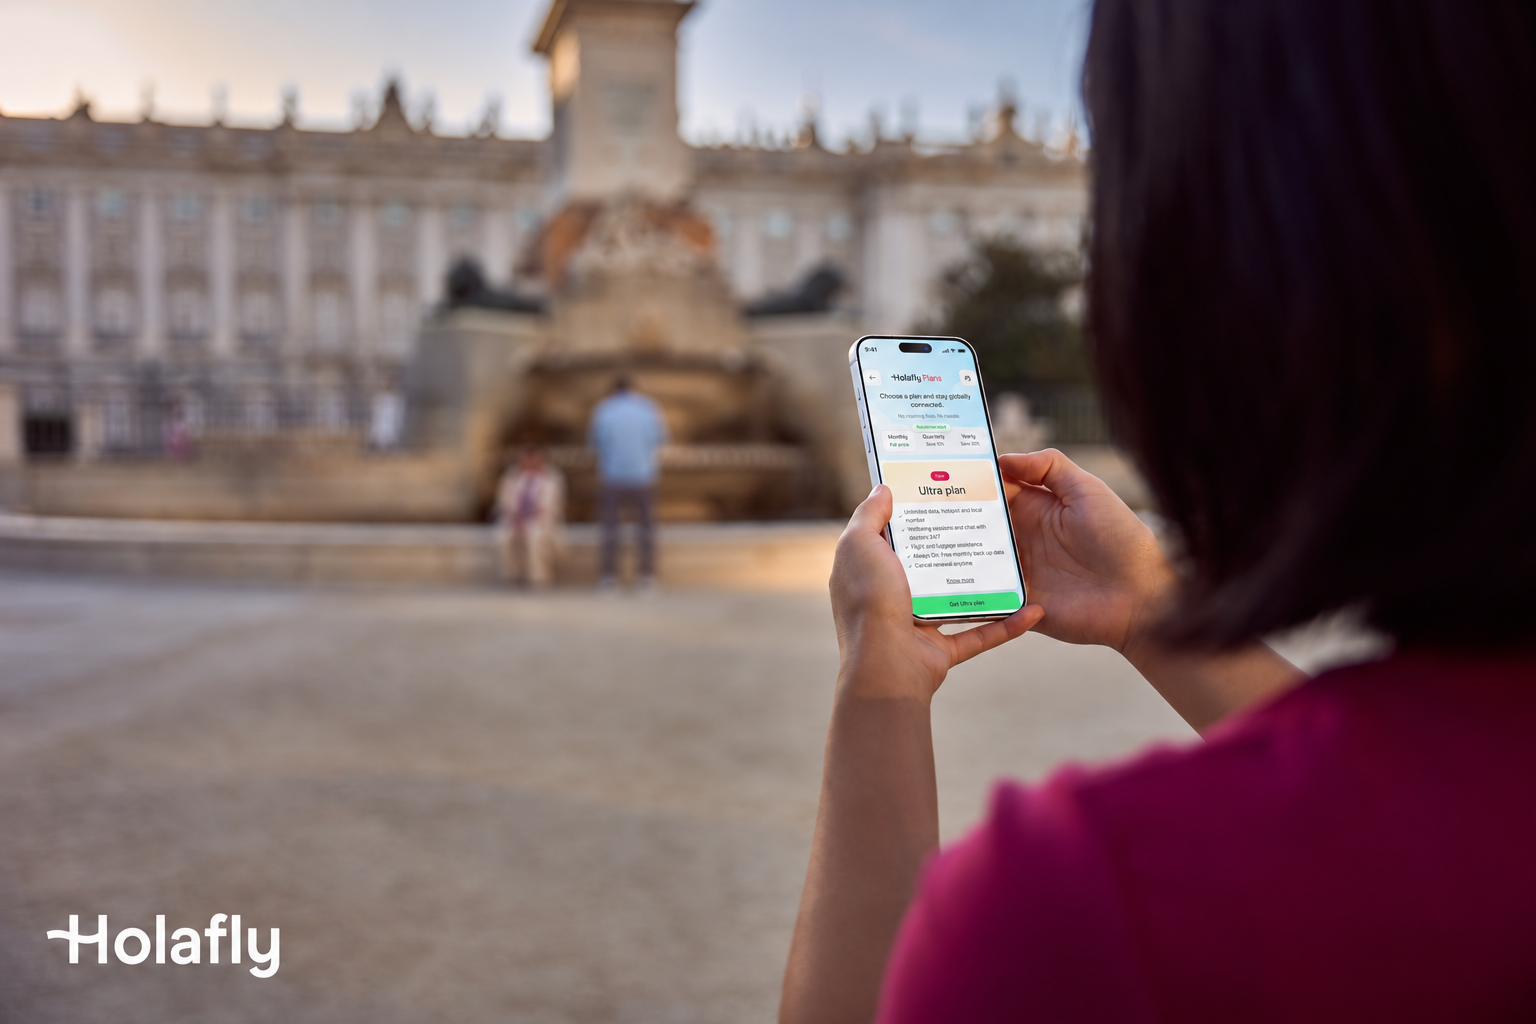
A new eSIM plan from Holafly offers travel support and healthcare with its new Ultra plan, ideal for business flyers and regular travellers.
Four couples, two old friends, and one night of romantic chaos. Here’s how to watch Friends Sex and Games online with Prime, from anywhere.
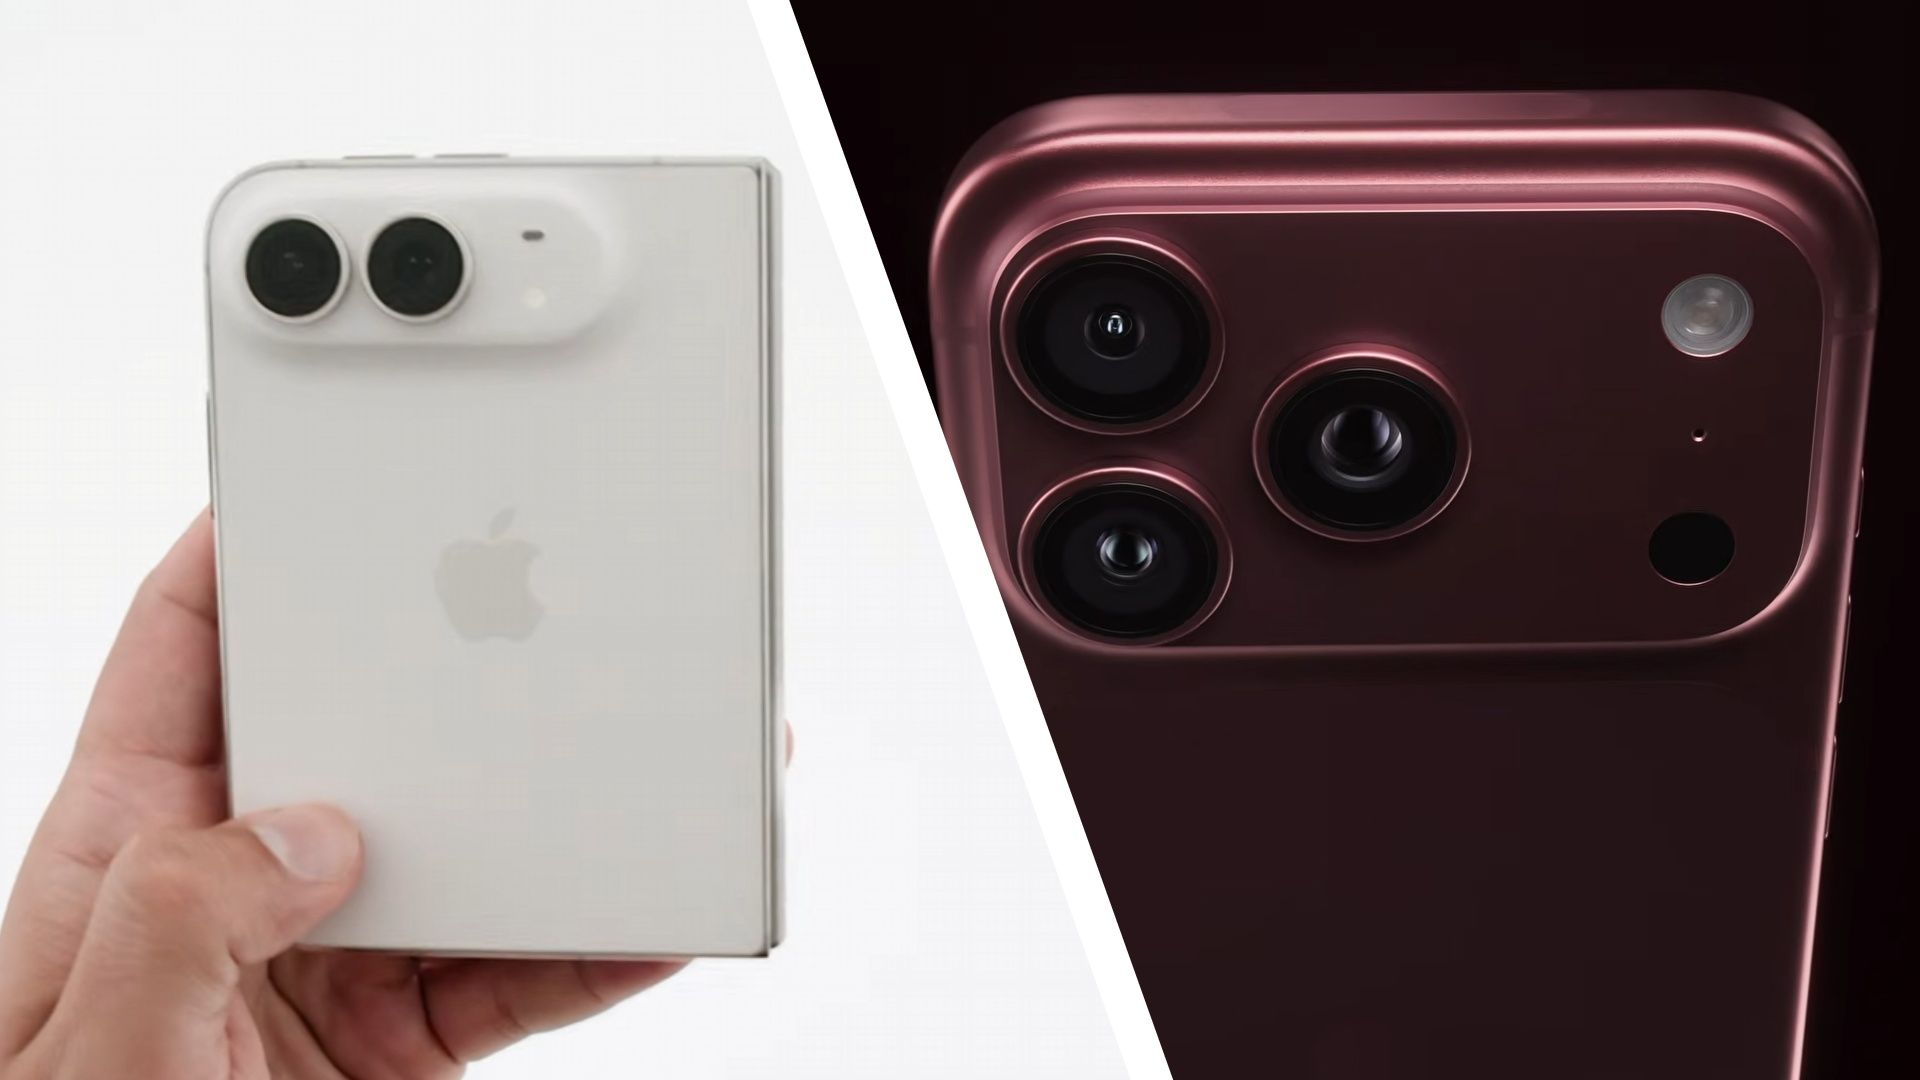
Avoid disappointment with these four tips
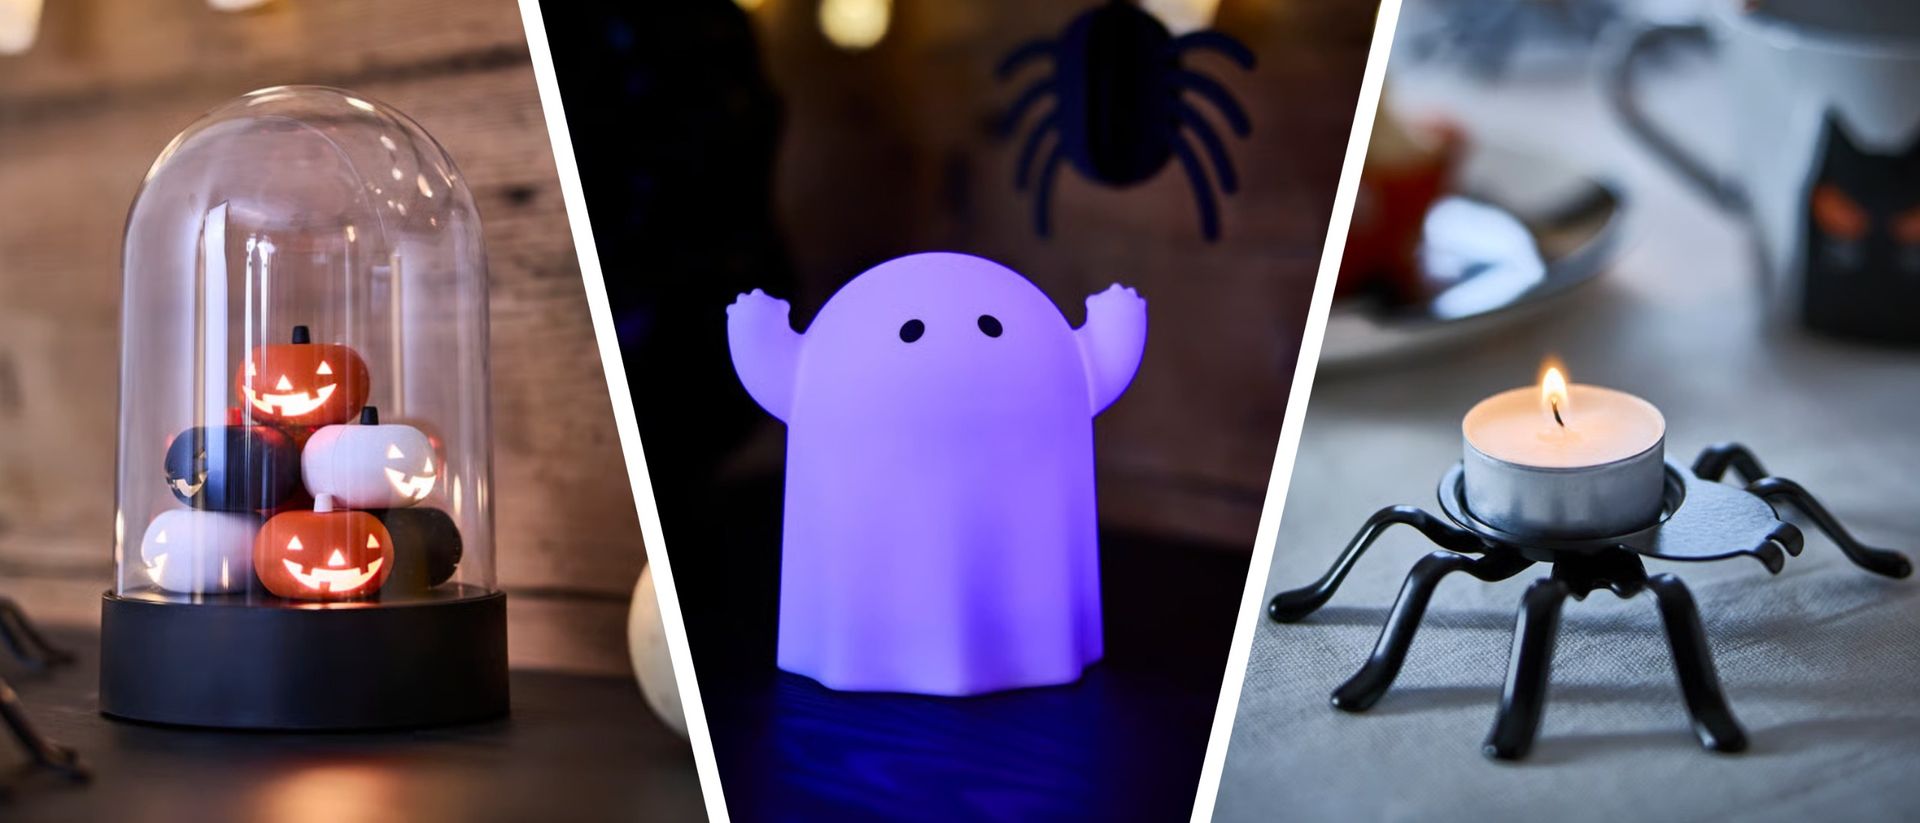
Halloween is knocking at the window, and my house is in dire need of a ghoulish makeover.
Hugging Face Blog

72 active sources
27 Turkish · 45 English
All sources


