

Hacker may have stolen millions in a malware attack against online poker players
Engadget (1 hour ago)

Wired has the story of a superuser cheating scandal.
Read the full story on Engadget.
Engadget (1 hour ago)
Wired has the story of a superuser cheating scandal.
Read the full story on Engadget.

The company says an unnamed third-party provider was compromised. Trading has resumed, and Polymarket says affected traders will be made whole.

Some attacks take real skill. Others just need someone to leave a door open. This week has both. Exposed passwords, old bugs still getting exploited, and trusted software doing things it shouldn’t. There’s a strange mix of clever tricks and careless mistakes.
A cleanup script deletes the malware’s own files, making the intrusion harder for the PC’s owner to detect. NordVPN’s Threat Intelligence team discovered malicious repositories posing as the KyttyPS5 and AnyPS5 emulators.
“We are still going to keep the data, but we will provide the decryption key for the hospital sector only.”

A newly identified advanced persistent threat (APT) group tracked as UAT-11473 was observed exploiting CVE-2026-20127, an authentication-bypass flaw in Cisco Catalyst SD-WAN Controllers, to deploy a custom malware framework called KeyDrift.

The leaked records include names, phone numbers, job titles, and assignments of thousands of ICE, CBP, and other DHS employees.
Adding sponsored content in more markets could make the feature profitable.
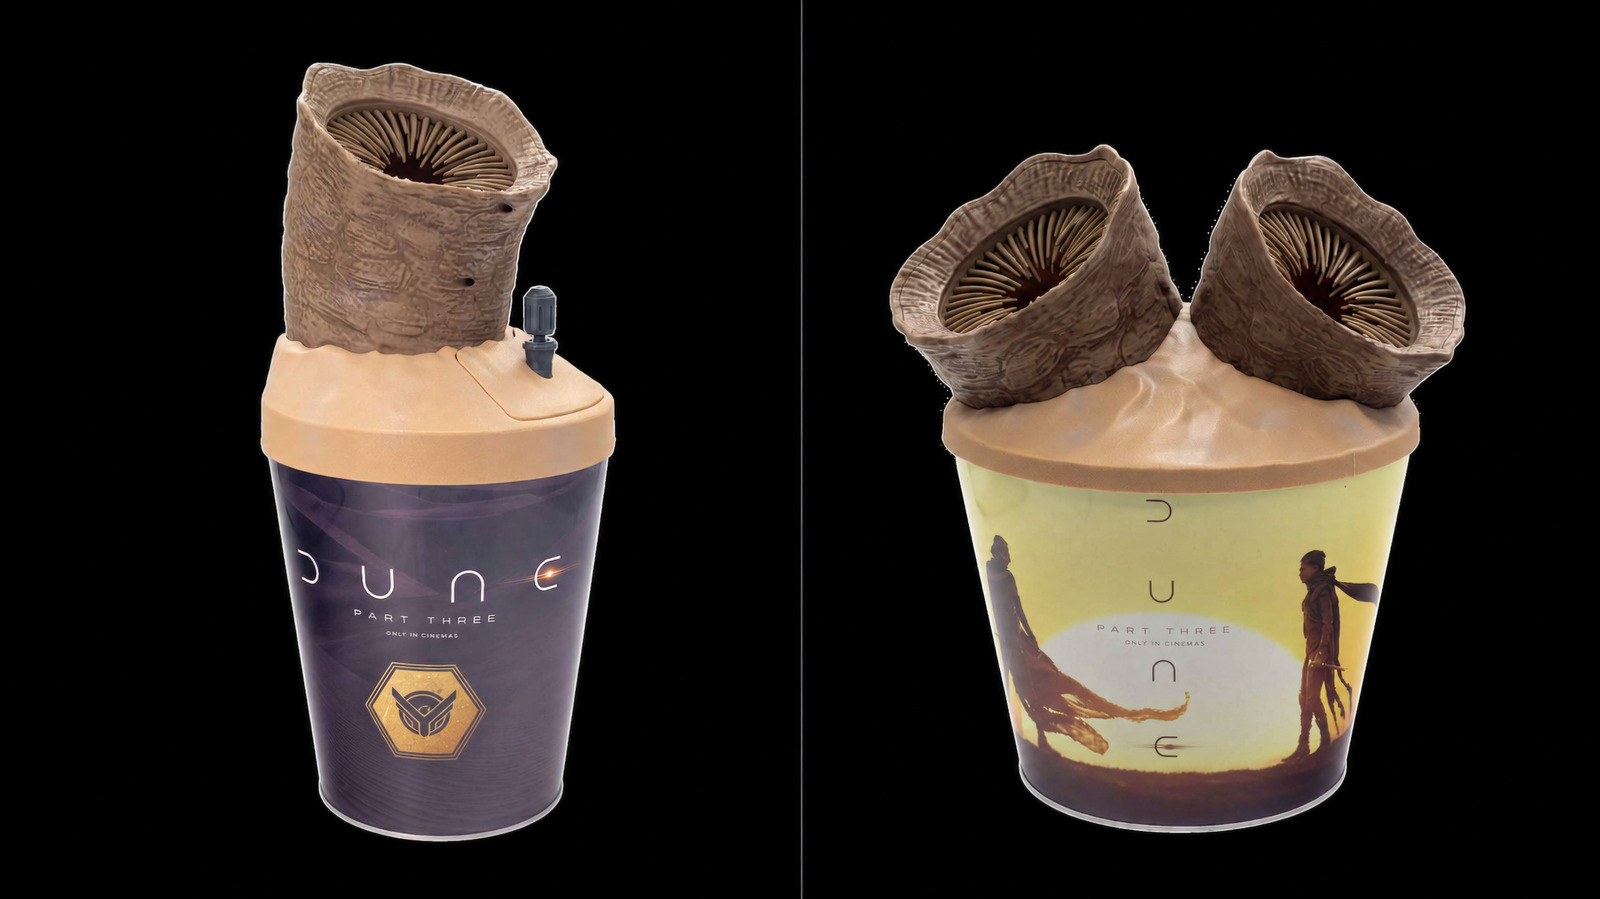
Just what the Sandworm bucket needed: a second hole.
The streamer also has an Assassin’s Creed series in the works, along with a Gears of War feature film.
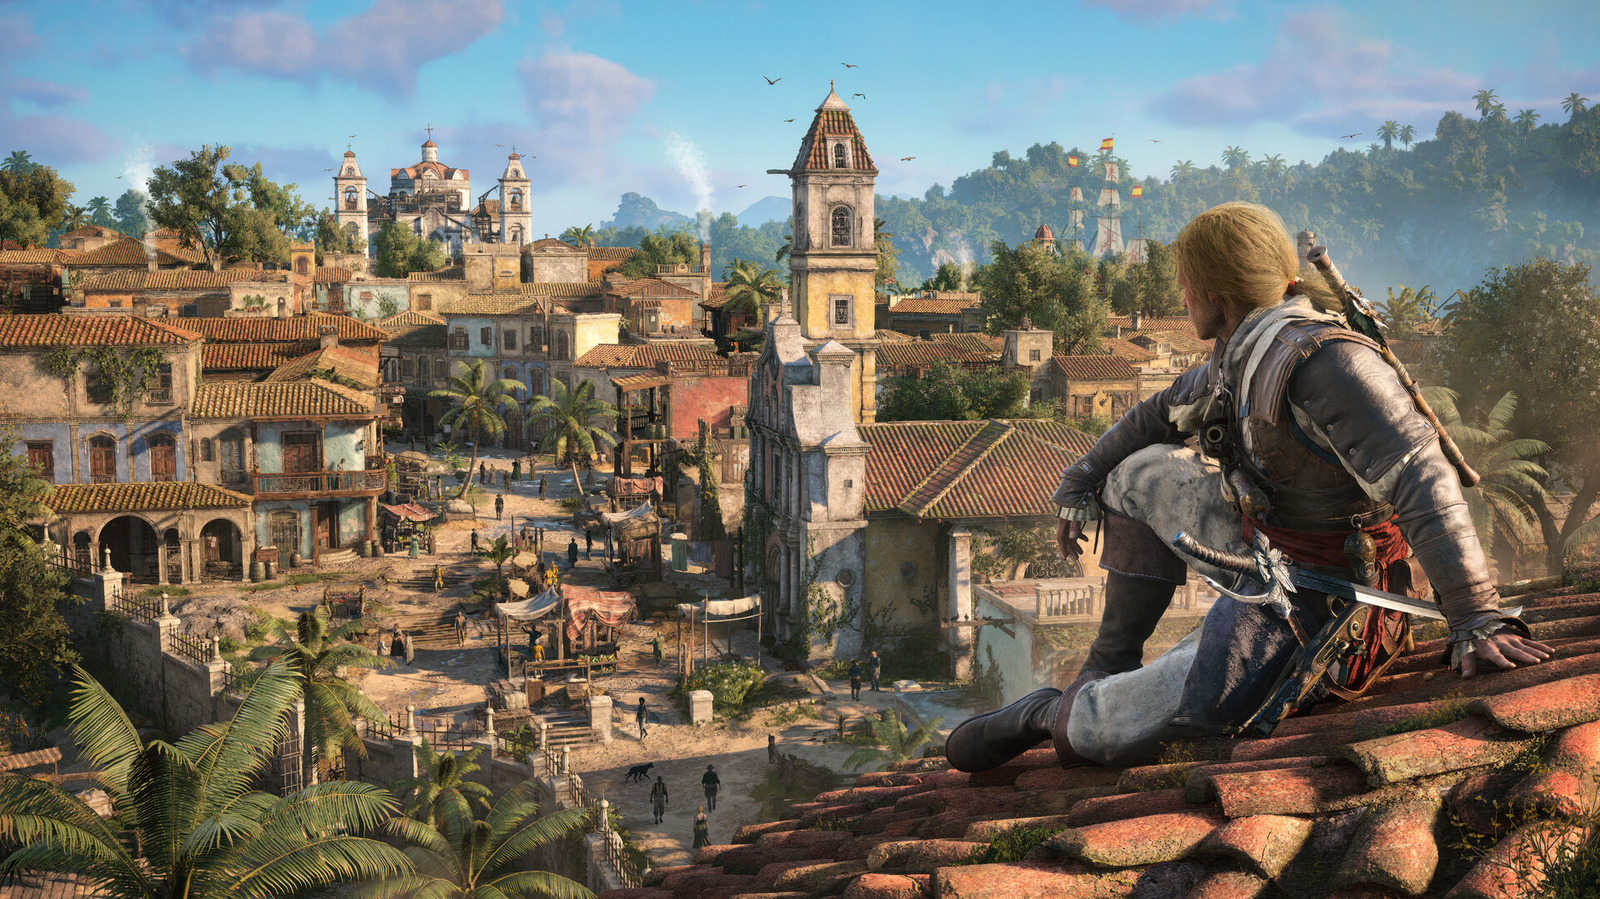
Ubisoft shared some updates on the franchise, including confirmation of a New Game+ option for Assassin’s Creed Valhalla.
71 active sources
26 Turkish · 45 English
All sources


