Recent UnrealIRCd Vulnerability Exploited in Attacks
Tracked as CVE-2026-114713, the high-severity flaw allows attackers to execute commands with server/IRCOp privileges.
Read the full story on SecurityWeek.
Tracked as CVE-2026-114713, the high-severity flaw allows attackers to execute commands with server/IRCOp privileges.
Read the full story on SecurityWeek.
Coles Group Limited, Australia’s second-largest retailer, is investigating what it described as a “cyber security incident” that has not impacted the company’s stores.
Vulncheck disclosed 14 vulnerabilities affecting Copeland XWEB EVO controllers, including two that threat actors quickly targeted.
Hackers compromised a third-party services provider and stole names, addresses, and driver’s license numbers.
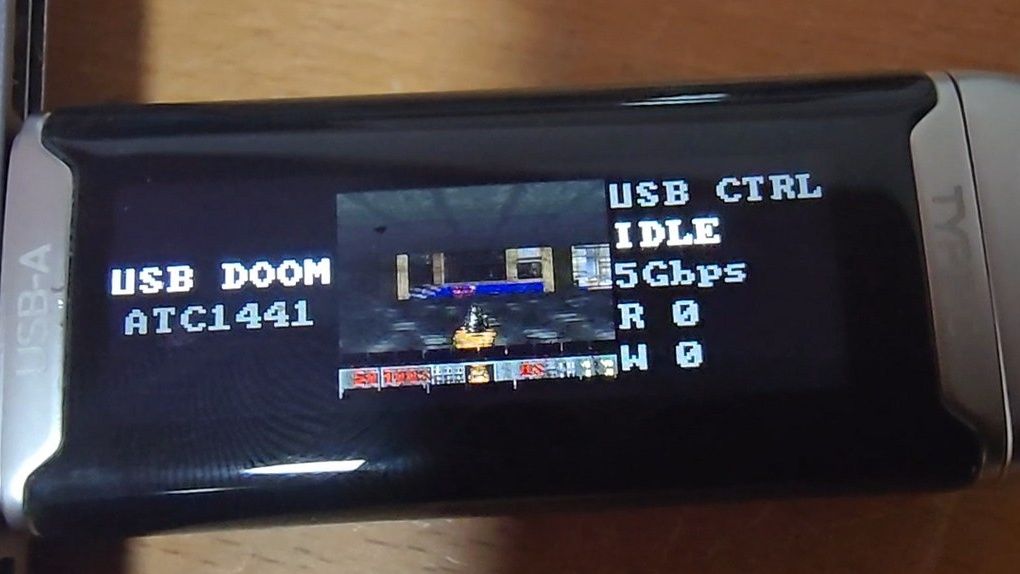
Aaron Christophel ported Doom to the LCD on a MOVESPEED MSSU10 flash drive and controls it with file transfers.
A financially motivated threat activity cluster tracked as REF3364 has been attributed to a Linux-focused cryptocurrency mining operation that tampers with the readings used to detect high GPU workloads.
An 11-year-old Linux kernel vulnerability, dubbed NoisyTCP, affects almost all Linux distributions and lets attackers crash systems running Nginx, Apache, and SSH servers with default configurations.
Tor 0.4.9.17 patches several security issues, including one related to how built-in DoS protections deal with IPv6.
Phishing emails posing as Microsoft 365 service notices referenced the real outage incident and threatened to delete held messages.
The move follows President Trump’s order to replace “artificial intelligence” with “super intelligence” in executive branch communications.
The directive protects smartphones as part of a person’s private sphere and requires “free and informed consent” for such access, the authority said.
MIT Technology Review AI
65 active sources
20 Turkish · 45 English
All sources