

Trump Mobile hack and apparent lack of FCC authorization raise security alarms
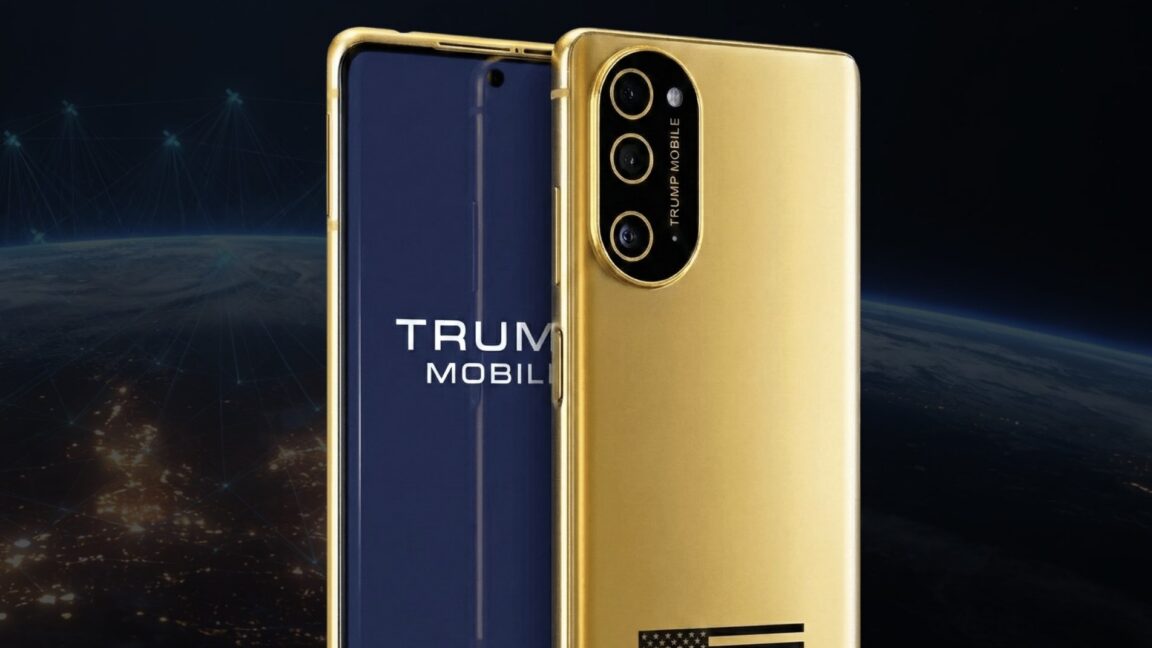
After hack and data breach, senator asks why Trump Mobile lacks some FCC filings.
Read the full story on Ars Technica.
After hack and data breach, senator asks why Trump Mobile lacks some FCC filings.
Read the full story on Ars Technica.

The scary surprises for the largest security update ever include security bypasses and unauthenticated RCEs.

A critical heap buffer overflow vulnerability (CVE-2026-39919) in the Ghostscript interpreter and rendering engine could allow remote code execution through specially crafted PDF files.
The Democratic People’s Republic of Korea (DPRK) is trying to get insight into its own war effort in Ukraine, through simple reply-baiting phishing attacks.

Today is Microsoft’s October 2026 Patch Tuesday, with security updates addressing a record-breaking 1,411 flaws, including one actively exploited and two publicly disclosed zero-day vulnerabilities.
CVE-2026-104935 affects Ivanti Connect Secure and it can be exploited for unauthenticated remote code execution with elevated privileges.
The U.K. Housing Ombudsman Service is investigating a third-party IT security incident that impacted its case management system on Tuesday.
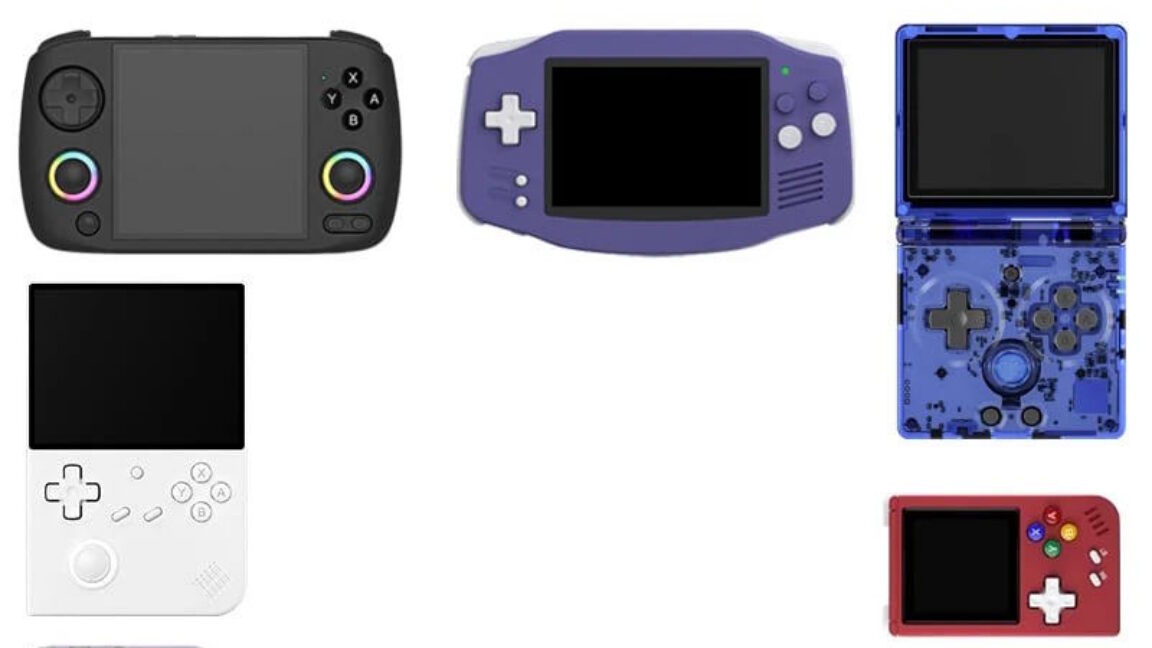
But third-party sellers, not Anbernic, are the ones routinely selling ROM-filled SD cards.
Topgolf and VMware “ran deep” before the migration.
US attorney apologized to court, said government has stopped running Trump ads.
Disney may acquire tech from one of the first chatbot makers linked to child suicide.
72 active sources
27 Turkish · 45 English
All sources







