Yandex confirms service outage as users lose access to cloud files
Russian cloud services provider Yandex announced that drone attacks damaged three of its data centers, forcing it to shut down two facilities and partially disable a third.
The proliferation of enterprise apps and the centrality of cloud identity providers requires an identity security rethink.
Doogee, Cubot, and other brands were allegedly compromised in production and tricked into shipping devices with malware.
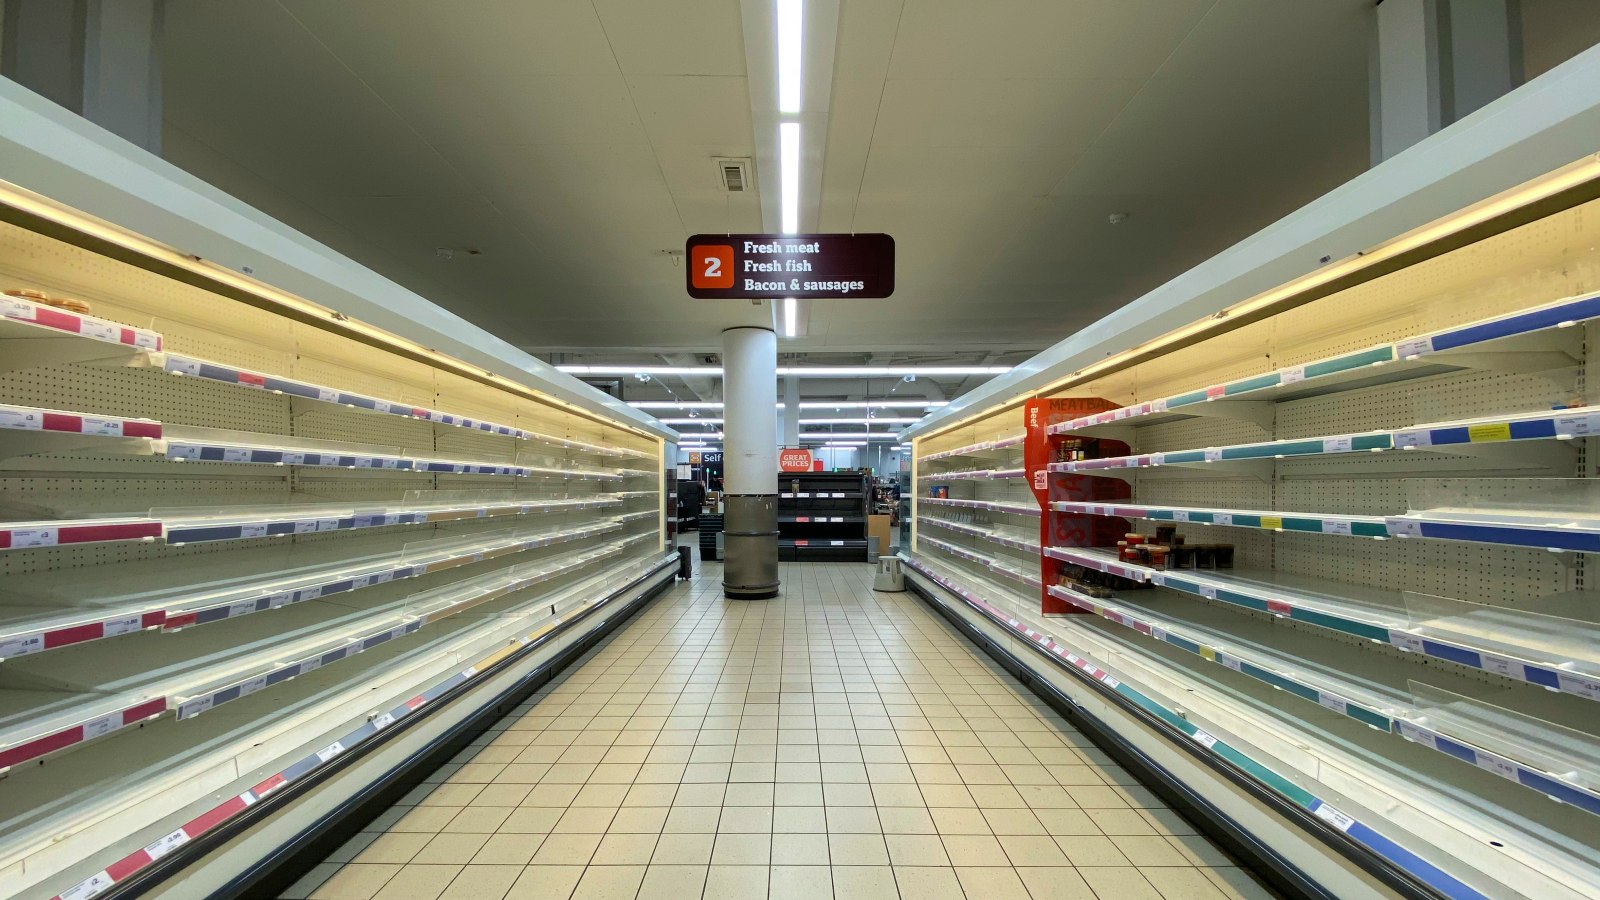
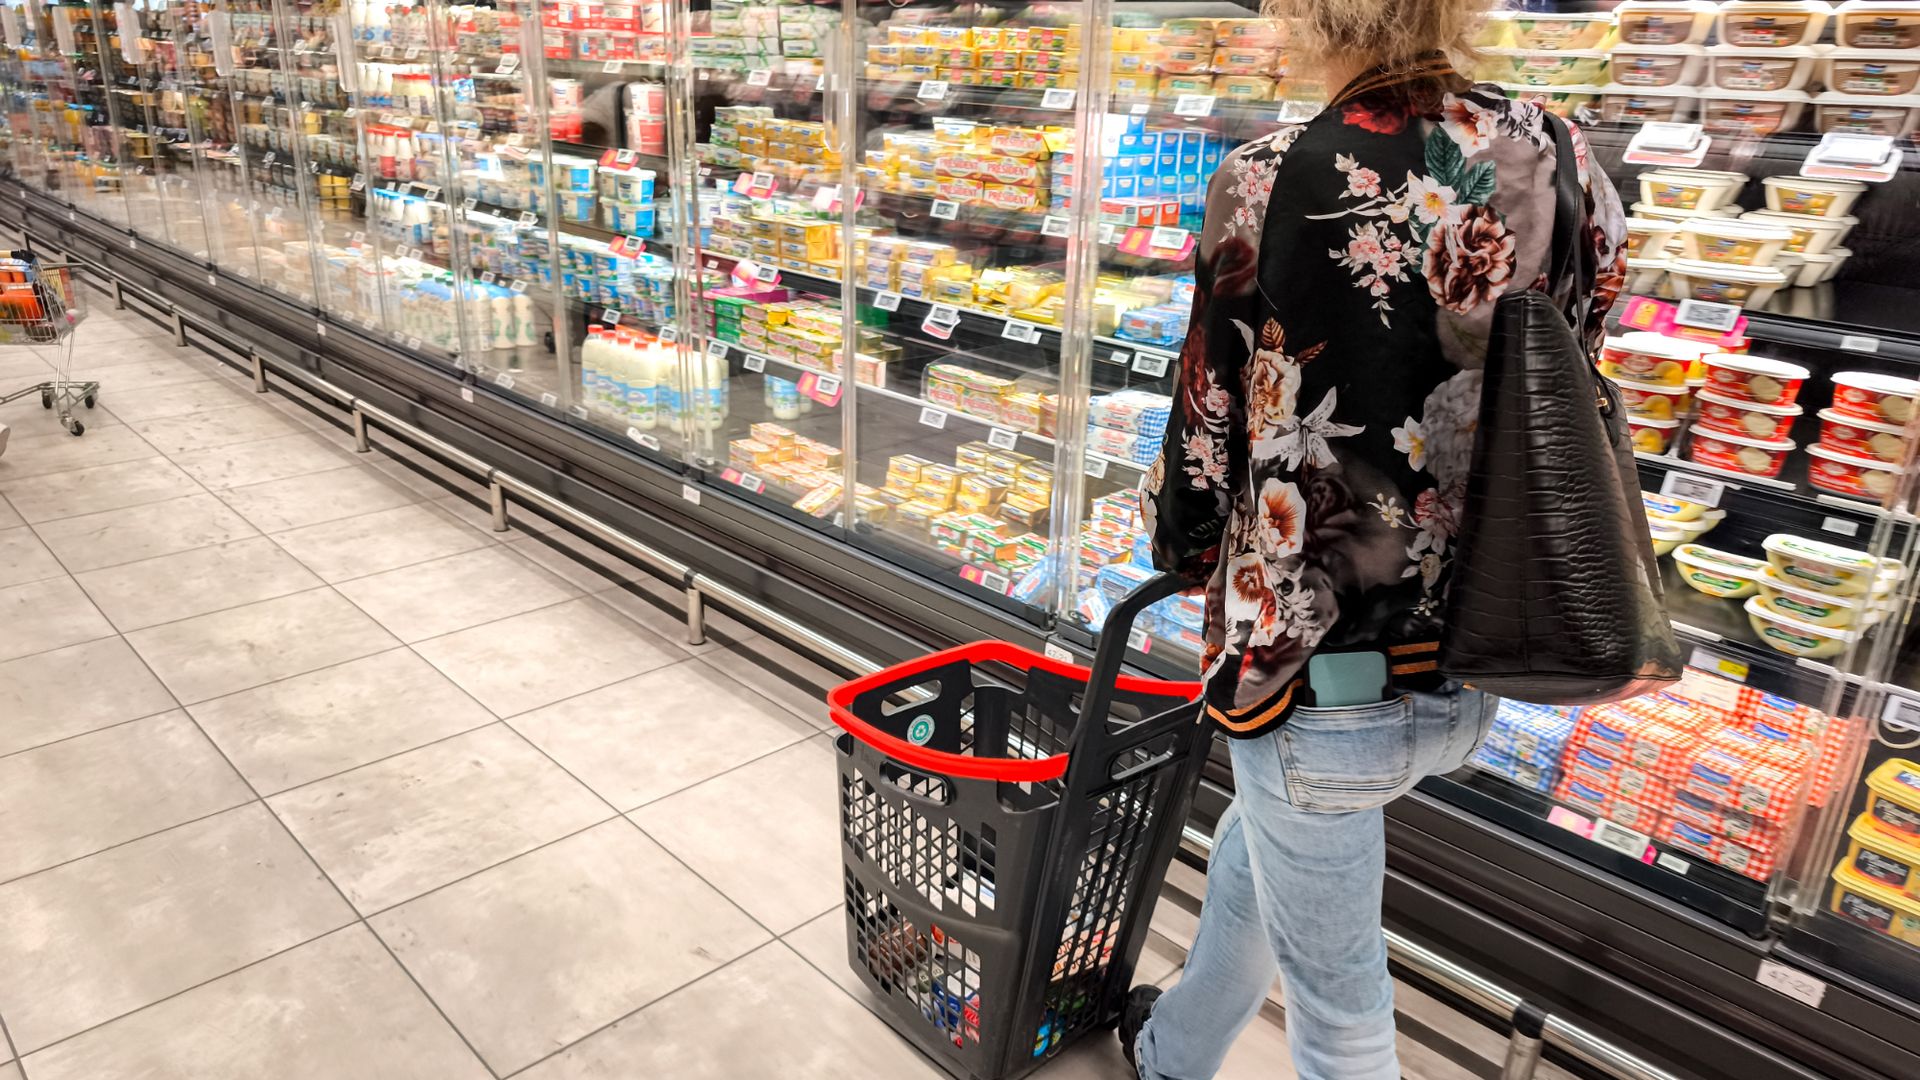
A spokesperson for the supermarket chain told Bloomberg that attackers infiltrated controls for the cooling systems and activated the defrost mode, which heated them to 50 degrees Celsius, or 122 degrees Fahrenheit. Roughly six hours passed before employees noticed.
No, that’s not a Power BI dashboard you’re looking at - that’s a ScreenConnect phishing lure.
IonQ has agreed to buy Elisity in an all-stock deal worth up to $1.3bn. Up to $150mn of that depends on how well Elisity does. The Maryland-based quantum computing company announced the deal on Monday. IonQ wants its security arm to guard against attacks aided by AI and, one day, quantum machines.
Attackers remotely defrosted refrigerators at multiple French supermarket chains overnight in a cyberattack that reportedly targeted Danfoss refrigeration controllers.
Some meetings last longer than it took attackers to jump on a newly disclosed security flaw this week. Within hours, they were already testing it. That’s not much time to read the warning, let alone do something about it. But speed is only part of the problem.
In September, hackers from a group called ShinyHunters announced that they stole a trove of FBI data about its own agents. It was an intelligence disaster. Last week, the FBI arrested (alternate link) someone associated with that crime.
Hackers broke into the refrigeration systems of hundreds of French supermarkets on Sunday night. Stores had to throw out meat, frozen goods and vegetables. About 150 Intermarché stores were hit, a spokesman for owner Groupement Mousquetaires told Bloomberg.
A new Windows malware loader called AvisLoader uses encrypted peer-to-peer communications to make command-and-control infrastructure harder to disrupt. Varonis researchers explain how the malware uses ClickFix delivery, shortcut-based persistence, and remote command execution capabilities.
Kanishka Narayan, concerned by Australian incident, says British cyber defences could be bypassed by AI agent UK politics live – latest updates An AI-driven cyber-attack like the OpenAI breach of Australia’s healthcare system is likely, “if not inevitable”, in the UK, according to a senior minister.
Retail giant Ahold Delhaize, one of the world’s largest food retail chains, confirmed today that it had to take some systems offline in response to a “cybersecurity incident” affecting its network.
The vulnerability tracked as CVE-2026-85097 can allow threat actors to take control of the targeted WordPress websites.
GitLab warned users today to immediately patch a maximum-severity vulnerability in the CI/CD Regular Expression Compiler that could let remote attackers run arbitrary code on targeted instances.
Surfshark has just launched its Black Friday VPN deal for 2026, offering savings on its popular One plan. But, is it worth the cost?
Fahmida Y Rashid will keep the momentum going as she leads Dark Reading.
Bitdefender Ultimate Small Business Security could be the cybersecurity co-worker to help you succeed
Kanishka Narayan said the government will use advanced AI to strengthen the UK against cyber attacks.
The outage hit the main Ubuntu and Canonical websites, including the Ubuntu blog and developer portal
A cyberattack has hit supermarkets in Europe, disabling refrigerators.
Oleg Korniev was a leader of YMCO, a sophisticated network of money mules that helped hackers move funds outside the US.
Hackers stole patients’ personal information, including names, addresses, email addresses, dates of birth, and phone numbers.
Threat actors have been observed exploiting a recently disclosed critical security flaw in SonicWall Secure Mobile Access (SMA) 1000 appliances within days of public disclosure.
72 active sources
27 Turkish · 45 English
All sources