Cybersecurity
Security Awareness Training Isn’t Dead, but It Needs a Rethink
All enterprises conduct security awareness training for their employees. But whether this has tangible benefits is debatable.
All enterprises conduct security awareness training for their employees. But whether this has tangible benefits is debatable.
Three country-code top-level domains were hijacked and used to impact several leading global brands.

Cybersecurity researchers have disclosed details of a targeted campaign aimed at South Korean financial organizations that used an artificial intelligence (AI) pen testing tool named ARTEX to carry out the attacks. The activity, per CrowdStrike Intelligence, was active from late September to early…
Threat actors have started targeting CVE-2026-21589, a critical vulnerability in Atlassian’s self-hosted Data Center products.
OAuth grants create data highways between SaaS apps, AI agents, and other tools. And, they are multiplying faster than any security team can review them. As the recent Klue breach showed, attackers are taking notice and exploiting forgotten OAuth grants to gain access to corporate data.
Suspected Chinese speaker used Claude Code and agentic pentesting tool ARTEX in attacks on South Korean lenders
A Maryland man was found guilty of stealing more than $53 million after hacking the decentralized crypto exchange Uranium Finance twice in April 2021.
Midnight Mimosa malware arrives pre-served.
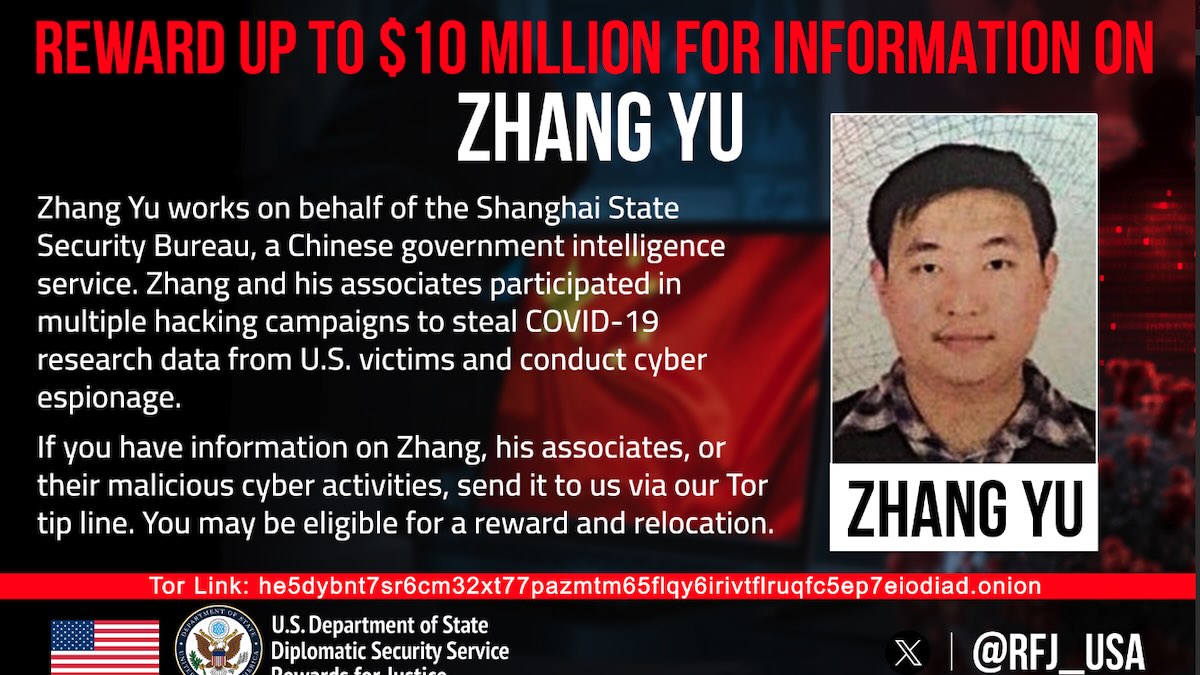
Zhang Yu was charged alongside Xu Zewei, who was extradited from Italy to the US in April 2026.
Critical and high-severity vulnerabilities could allow attackers to bypass authentication, execute arbitrary code, and elevate their privileges.
Microsoft will soon introduce support for third-party deepfake detection solutions and impersonation protection in Teams meetings.
The United States Department of Justice has charged Zohar Pinhasi, 50, also known as “Zack Silver” and “Zack Green,” with fraud. He ran a Florida-based company called MonsterCloud that told ransomware victims not to pay attackers because it had a way of decrypting their files – for a fee, of course.
Dark Reading is about to begin a new decade in its storied history, and we have some breaking news of our own to share.
ASOS is sending updates to affected customers about the cybersecurity incident it suffered earlier this week, confirming that hackers accessed some personal data.
Security pact promises information-sharing and coordinated disruption, but offers little detail on agencies or funding
This essay was written with Seva Gunitsky, and originally appeared in Foreign Affairs. Two weeks after Moscow’s full-scale invasion of Ukraine in March 2022, the Russian TV Channel One editor Marina Ovsyannikova burst onto the set of the evening newscast. She held up a hand-drawn sign behind the…

Cyber resilience now depends on how quickly leaders can understand, decide and recover.

Phishing kits are no longer limited to copying a familiar login page and waiting for a victim to enter credentials. Attackers are increasingly building filtering, session management, and traffic controls into the infrastructure that delivers the phishing page itself. ANY.RUN has identified Wazza, a…
The co-creator of Empire Market, one of the largest dark web marketplaces before its shutdown, has been sentenced to 40 years in prison for facilitating $430 million in illegal transactions from 2018 to 2020.

Cybersecurity researchers have discovered a cluster of 16 malicious Mozilla Firefox extensions that are capable of stealing cryptocurrency wallet recovery phrases and private keys. “The extensions masquerade as wallet portals, desktop utilities, and browser tools, but their code intercepts recovery…
Zohar Pinhasi was paying ransoms to obtain decryption keys and then charging victims substantially more for remediation.
The figure is far higher than the counts that surfaced in earlier filings and patient notifications.
Attackers are creating new accounts and deleting existing ones and passwords to prevent legitimate access.
72 active sources
27 Turkish · 45 English
All sources